Speaking
Agent governance, confidential computing, and what a system can actually prove.
What I speak about
I speak about what agent systems can actually prove, not what they claim. Talks are technical, demo-led, and usually carry a negative result alongside the working one.
Runtime governance for AI agents
Where enforcement sits between an agent's decision and its action, and what a policy gate can express that a prompt cannot.
Hardware attestation, and its limits
Validated on live SEV-SNP, TDX and H100. Including the part most talks skip: no confidential computing silicon is proof against someone who owns the machine.
Verifiable evidence and audit chains
Tamper-evident records a third party can check offline, and the difference between proving what happened and preventing it.
Model weight custody
What changes when the model leaves your data center, and why open weights do not end the custody problem.
Author of Architecting at Scale (Packt, 2026), a field guide to large-scale AI-native system design.
Organising something and think this fits? Get in touch. Contact
Coming up
- 9 Sep 2026 The Verifiable Agent Virtual BriefingVerifiable Agent Summit · Online
- 15 Sep 2026 AgenTrust: From Governance Decisions to Verifiable Agent ActionsGenAI Gurus · Online
- 30 Sep 2026 Weight Custody Manifest: When the Model Leaves Your Data Center, the Threat Model FlipsAAIF Community Showcase, Agentic AI Foundation · Online
- 6 Oct 2026 Governed MCP: Cedar Policy Enforcement and TEE Attestation for Enterprise Tool CallsMCP Dev Summit Toronto 2026 · Toronto, Canada
- 15 Oct 2026 Your Root of Trust Is an Unhardened Parser: A Post-Mortem on My Own Attestation CodeAI Security Summit, San Francisco · San Francisco, CA
- 30 Oct 2026 Verifiable Agent SummitVerifiable Agent Summit · San Francisco, CA
Proof videos
Short, evidence-led demonstrations of what trustworthy AI systems can actually prove.
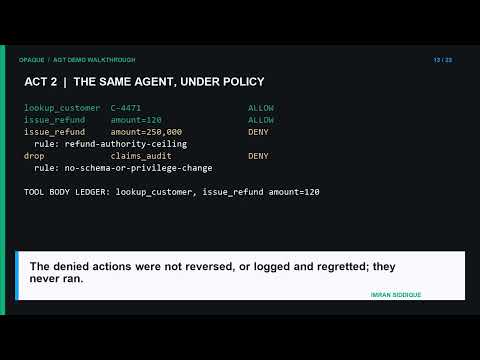
AGT Runtime Guardrail: A Fully Offline Demo
Enforcement with no network
Your Policy Engine Can Lie — Verify the Policy Hash
Checking the policy the engine actually loaded
 Short
Change One Byte. This Model Refuses to Load.
Tamper detection in under a minute
Open Weights Don't End the Custody Problem — Watch Tampering Fail
Model custody, demonstrated
Past talks
9 of 9 recorded
AGT (Agent Governance Toolkit): The Runtime Guardrail, What and Why
PRONATIVE AI Keynote Series
Proof, Not Promises: Attesting What Your AI Agent Is
Identerati Office Hours, episode 220
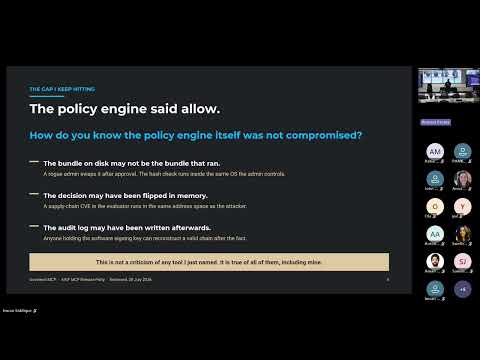
Policy Enforcement and Tamper-Evident Audit Chains
MCP Release Party, Seattle
From Trust to Proof: The Next Generation of AI Agent Governance
OPAQUE AI Confidential Webinar
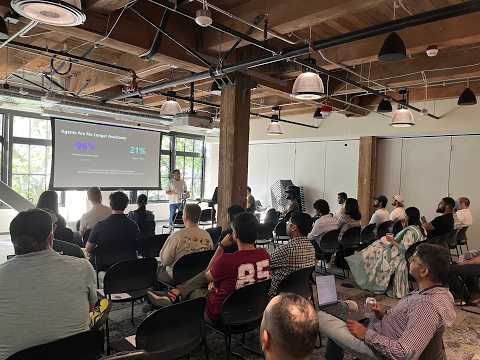
Cloud Native Seattle Meetup, June 2026
Cloud Native Seattle
Governing AI Agents at the Hardware Boundary
Confidential Computing Summit 2026
Governance for AI Agents
Open Source Friday, GitHub
Governing AI Agents at Runtime: Open Source Zero-Trust with AGT
Ubuntu Summit 26.04
Building Governed AI Agents with the Microsoft Agent Governance Toolkit
GenAI Gurus